CentOS基线脚本,三级等保服务器系统安全配置脚本_centos 日志 等保三
fi
if [ -z $sysadmin ];then
useradd sysadmin
echo sysadmin:In123!@#123|chpasswd
fi
shenji=cat /etc/passwd |grep shenji | grep -v ^# | cut -d: -f 1
anquan=cat /etc/passwd |grep anquan | grep -v ^# | cut -d: -f 1
sysadmin=cat /etc/passwd |grep sysadmin | grep -v ^# | cut -d: -f 1
if [ -z $shenji -o -z $anquan -o -z $sysadmin ];then
echo “…[N] Authorized user: $shenji, $anquan, $sysadmin”
else
echo “…[Y] Authorized user: $shenji, $anquan, $sysadmin”
fi
}
#检查登录失败锁定配置CentOS
function CheckLoginFailureLock_CentOS() {
Login_Failure_Lock=grep "pam\_tally2.so" /etc/pam.d/system-auth| grep -v ^#|head -n 1|awk '{print $7}'
if [ -z $Login_Failure_Lock ];then
sed -i ‘/pam_tally2.so/s/#auth/auth/g’ /etc/pam.d/system-auth
Login_Failure_Lock=grep "pam\_tally2.so" /etc/pam.d/system-auth| grep -v ^#|head -n 1|awk '{print $7}'
fi
if [ -z Login_Failure_Lock];thensed−i′Login\_Failure\_Lock ];then
sed -i 'Login_Failure_Lock];thensed−i′a auth required pam_tally2.so onerr=fail audit silent dent=5 unlock_time=600 even_deny_root root_unlock_time=600’ /etc/pam.d/system-auth
else
Login_Failure_Lock=grep "pam\_tally2.so onerr=fail audit silent dent=5 unlock\_time=600" /etc/pam.d/system-auth| grep -v ^#|awk '{print $7}'
if [ -z KaTeX parse error: Expected 'EOF', got '#' at position 60: …lly2.so/s/auth/#̲auth/g' /etc/pa…a auth required pam_tally2.so onerr=fail audit silent dent=5 unlock_time=600 even_deny_root root_unlock_time=600’ /etc/pam.d/system-auth
fi
fi
Login_Failure_Lock=grep "pam\_tally2.so onerr=fail audit silent dent=5 unlock\_time=600" /etc/pam.d/system-auth| grep -v ^#|awk '{print $7","$8","$10}'
if [ -z $Login_Failure_Lock ];then
echo “…[N] Login Failure Lock: Reset failed”
else
echo “…[Y] Login Failure Lock: $Login_Failure_Lock”
fi
}
#检查登录失败锁定配置SUSE
function CheckLoginFailureLock_SUSE() {
Login_Failure_Number=cat /etc/login.defs | grep LOGIN\_RETRIES | grep -v ^# | awk '{print $2}'
if [ -z $Login_Failure_Number ];then
sed -i ‘s/#LOGIN_RETRIES/LOGIN_RETRIES/’ /etc/login.defs
Login_Failure_Number=cat /etc/login.defs | grep LOGIN\_RETRIES | grep -v ^# | awk '{print $2}'
fi
if [ -z $Login_Failure_Number ];then
echo “…[N] Number of login failures: No configuration”
elif [ $Login_Failure_Number -le 8 -a $Login_Failure_Number -ge 3 ];then
echo “…[Y] Number of login failures: Login_Failure_Number"elsesed−i′/LOGIN_RETRIES/s/′"Login\_Failure\_Number"
else
sed -i '/LOGIN\_RETRIES/s/'"Login_Failure_Number"elsesed−i′/LOGIN_RETRIES/s/′"{Login_Failure_Number}”‘/5/g’ /etc/login.defs
Login_Failure_Number=cat /etc/login.defs | grep LOGIN\_RETRIES | grep -v ^# | awk '{print $2}'
if [ $Login_Failure_Number -le 8 -a $Login_Failure_Number -ge 3 ];then
echo “…[Y] Number of login failures: $Login_Failure_Number”
else
echo “…[N] Number of login failures: No configuration”
fi
fi
Login_Failure_Time=cat /etc/login.defs | grep LOGIN\_TIMEOUT | grep -v ^# | awk '{print $2}'
if [ -z $Login_Failure_Time ];then
sed -i ‘s/#LOGIN_TIMEOUT/LOGIN_TIMEOUT/’ /etc/login.defs
Login_Failure_Time=cat /etc/login.defs | grep LOGIN\_TIMEOUT | grep -v ^# | awk '{print $2}'
fi
if [ -z $Login_Failure_Time ];then
echo “…[N] Login failure lock time: Reset failed”
elif [ $Login_Failure_Time -le 1800 -a $Login_Failure_Time -ge 300 ];then
echo “…[Y] Login failure lock time: Login_Failure_Timeseconds"elsesed−i′/LOGIN_TIMEOUT/s/′"Login\_Failure\_Time seconds"
else
sed -i '/LOGIN\_TIMEOUT/s/'"Login_Failure_Timeseconds"elsesed−i′/LOGIN_TIMEOUT/s/′"{Login_Failure_Time}”‘/300/g’ /etc/login.defs
Login_Failure_Time=cat /etc/login.defs | grep LOGIN\_TIMEOUT | grep -v ^# | awk '{print $2}'
if [ $Login_Failure_Time -le 1800 -a $Login_Failure_Time -ge 300 ];then
echo “…[Y] Login failure lock time: $Login_Failure_Time seconds”
else
echo “…[N] Login failure lock time: Reset failed”
fi
fi
}
#检查密码策略CentOS
function CheckPasswordPolicy_CentOS() {
Password_Policy=grep "pam\_cracklib.so" /etc/pam.d/system-auth| grep -v ^#|awk '{print $4}'
if [ -z $Password_Policy ];then
sed -i ‘/pam_cracklib.so/s/#password/password/g’ /etc/pam.d/system-auth
Password_Policy=grep "pam\_cracklib.so" /etc/pam.d/system-auth| grep -v ^#|awk '{print $4}'
fi
if [ -z Password_Policy];thensed−i′Password\_Policy ];then
sed -i 'Password_Policy];thensed−i′a password requisite pam_cracklib.so minlen=8 ucredit=-1 lcredit=-1 dcredit=-1 ocredit=-1’ /etc/pam.d/system-auth
else
Password_Policy=grep "pam\_cracklib.so minlen=8 ucredit=-1 lcredit=-1 dcredit=-1 ocredit=-1" /etc/pam.d/system-auth| grep -v ^#|awk '{print $4}'
if [ -z KaTeX parse error: Expected 'EOF', got '#' at position 62: ….so/s/password/#̲password/g' /et…a password requisite pam_cracklib.so minlen=8 ucredit=-1 lcredit=-1 dcredit=-1 ocredit=-1’ /etc/pam.d/system-auth
fi
fi
Password_Policy=grep "pam\_cracklib.so minlen=8 ucredit=-1 lcredit=-1 dcredit=-1 ocredit=-1" /etc/pam.d/system-auth| grep -v ^#|awk '{print $4","$5","$6","$7","$8}'
if [ -z $Password_Policy ];then
echo “…[N] Password Policy: Reset failed”
else
echo “…[Y] Password Policy: $Password_Policy”
fi
}
#检查密码策略SUSE
function CheckPasswordPolicy_SUSE() {
Password_Policy=grep "pam\_cracklib.so" /etc/pam.d/common-password| grep -v ^#|awk '{print $4}'
if [ -z $Password_Policy ];then
sed -i ‘/pam_cracklib.so/s/#password/password/g’ /etc/pam.d/common-password
Password_Policy=grep "pam\_cracklib.so" /etc/pam.d/common-password| grep -v ^#|awk '{print $4}'
fi
if [ -z Password_Policy];thensed−i′Password\_Policy ];then
sed -i 'Password_Policy];thensed−i′a password requisite pam_cracklib.so retry=3 difok=3 minlen=8 ucredit=-1 lcredit=-1 dcredit=-1 ocredit=-1’ /etc/pam.d/common-password
else
Password_Policy=grep "minlen=8 ucredit=-1 lcredit=-1 dcredit=-1 ocredit=-1" /etc/pam.d/common-password| grep -v ^#|awk '{print $4}'
if [ -z KaTeX parse error: Expected 'EOF', got '#' at position 62: ….so/s/password/#̲password/g' /et…a password requisite pam_cracklib.so retry=3 difok=3 minlen=8 ucredit=-1 lcredit=-1 dcredit=-1 ocredit=-1’ /etc/pam.d/common-password
fi
fi
Password_Policy=grep "minlen=8 ucredit=-1 lcredit=-1 dcredit=-1 ocredit=-1" /etc/pam.d/common-password| grep -v ^#|awk '{print $4","$5","$6","$7","$8}'
if [ -z $Password_Policy ];then
echo “…[N] Password Policy: Reset failed”
else
echo “…[Y] Password Policy: $Password_Policy”
fi
}
#检查日志服务CentOS
function CheckLogService_CentOS() {
Log_Service=systemctl status rsyslog | grep active | awk '{print $3}'
if [ $Log_Service != “(running)” ];then
systemctl start rsyslog
systemctl enable rsyslog
fi
Log_Service=systemctl status rsyslog | grep active | awk '{print $3}'
if [ $Log_Service = “(running)” ];then
echo “…[Y] Log Service: $Log_Service”
else
echo “…[N] Log Service: $Log_Service”
fi
}
#检查日志服务SUSE
function CheckLogService_SUSE() {
Log_Service=systemctl status syslog-ng | grep active | awk '{print $3}'
if [ $Log_Service != “(running)” ];then
systemctl start syslog-ng
systemctl enable syslog-ng
fi
Log_Service=systemctl status syslog-ng | grep active | awk '{print $3}'
if [ $Log_Service = “(running)” ];then
echo “…[Y] Log Service: $Log_Service”
else
zypper install syslog-ng -y 2>/dev/null
systemctl start syslog-ng
systemctl enable syslog-ng
Log_Service=systemctl status syslog-ng | grep active | awk '{print $3}'
if [ $Log_Service = “(running)” ];then
echo “…[Y] Log Service: $Log_Service”
else
echo “…[N] Log Service: Reset failed”
fi
fi
}
#停用telnet-server服务
function CheckTelnetServer() {
Telnet_Server=rpm -qa|grep telnet-server
if [ -z $Telnet_Server ];then
echo “…[Y] Telnet Server: Not installed”
else
systemctl stop telnet.socket
systemctl disable telnet.socket
echo “…[Y] Telnet Server: disable”
fi
}
main() {
CheckSystem
system_v=echo $var | cut -d " " -f 2
if [ $system_v = “CentOS” -o $system_v = “TencentOS” ];then
CheckPassMaxDays
CheckLogBackupTime
CheckConnectionTimeout
CheckSharedUser
CheckAuthorizedUser
CheckAuditLogs
CheckLogService_CentOS
自我介绍一下,小编13年上海交大毕业,曾经在小公司待过,也去过华为、OPPO等大厂,18年进入阿里一直到现在。
深知大多数网络安全工程师,想要提升技能,往往是自己摸索成长,但自己不成体系的自学效果低效又漫长,而且极易碰到天花板技术停滞不前!
因此收集整理了一份《2024年网络安全全套学习资料》,初衷也很简单,就是希望能够帮助到想自学提升又不知道该从何学起的朋友。
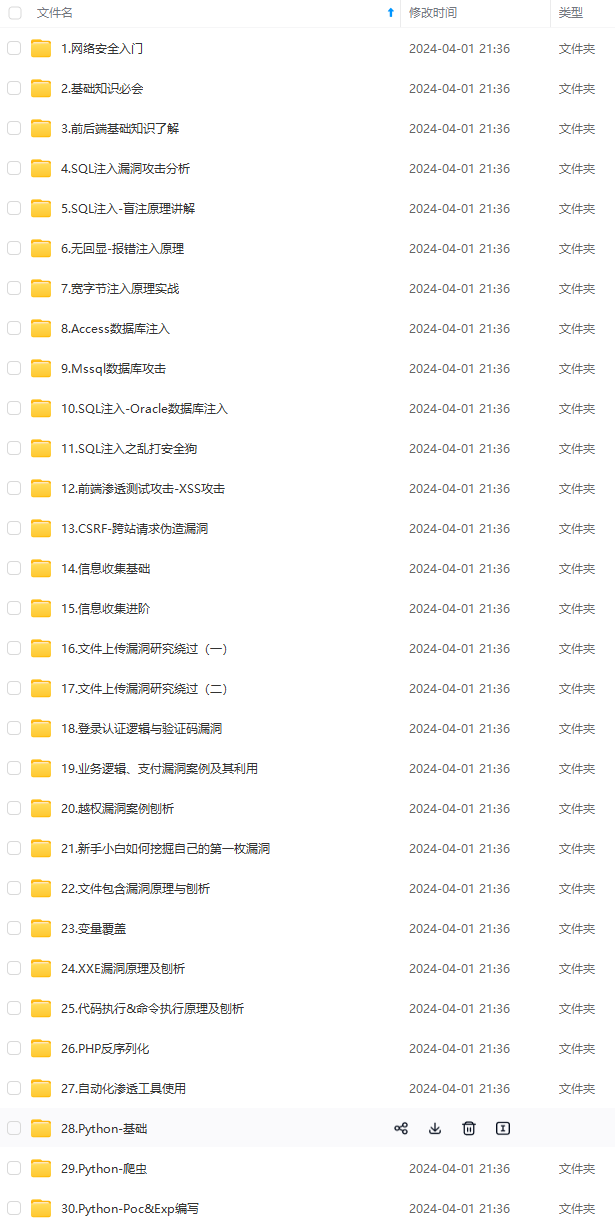
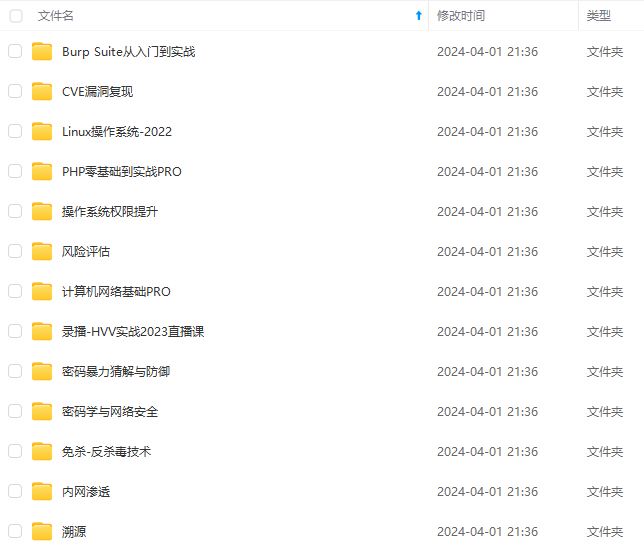
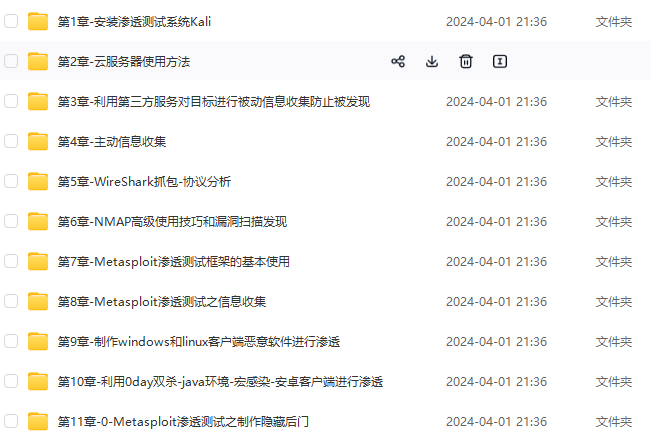
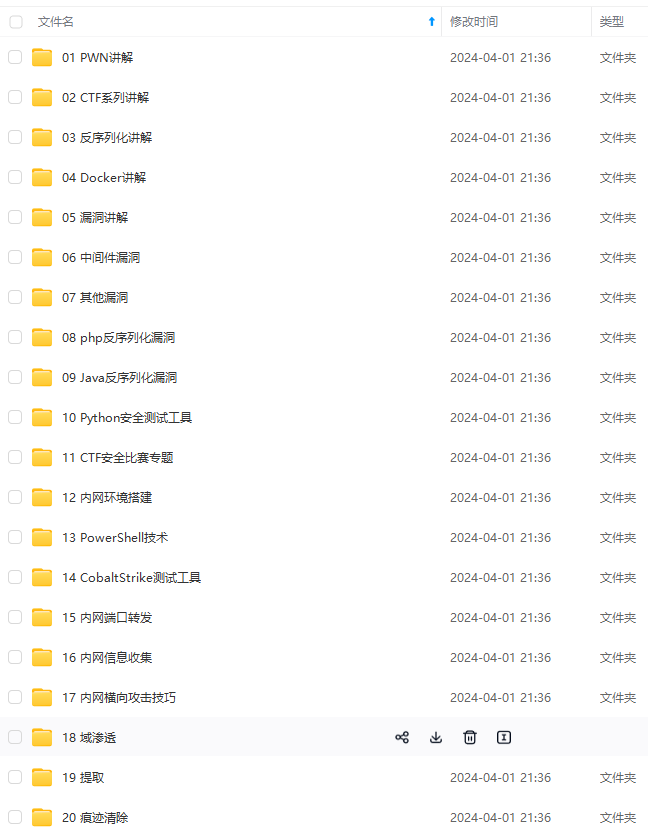
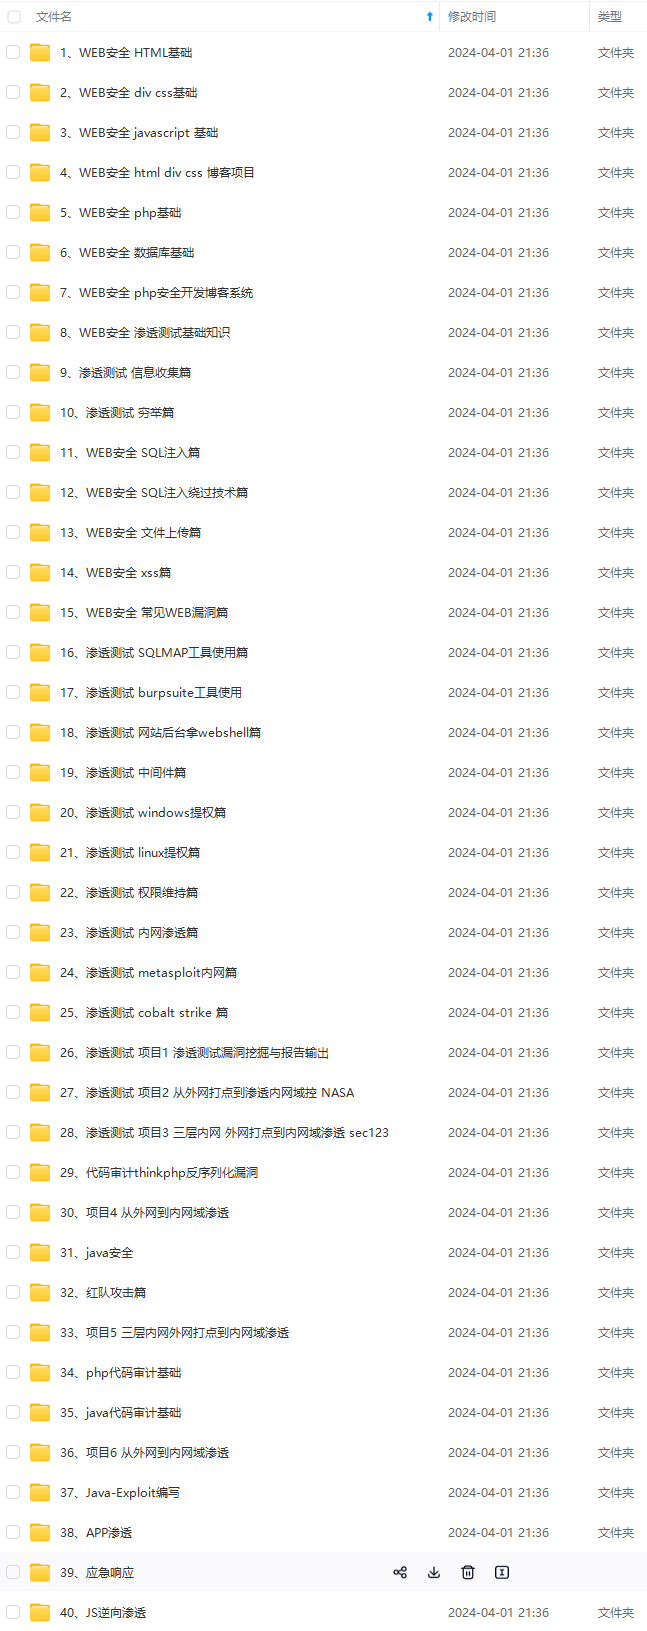
既有适合小白学习的零基础资料,也有适合3年以上经验的小伙伴深入学习提升的进阶课程,基本涵盖了95%以上网络安全知识点,真正体系化!
由于文件比较大,这里只是将部分目录大纲截图出来,每个节点里面都包含大厂面经、学习笔记、源码讲义、实战项目、讲解视频,并且后续会持续更新
如果你觉得这些内容对你有帮助,可以添加VX:vip204888 (备注网络安全获取)
给大家的福利
零基础入门
对于从来没有接触过网络安全的同学,我们帮你准备了详细的学习成长路线图。可以说是最科学最系统的学习路线,大家跟着这个大的方向学习准没问题。

同时每个成长路线对应的板块都有配套的视频提供:

因篇幅有限,仅展示部分资料
一个人可以走的很快,但一群人才能走的更远。不论你是正从事IT行业的老鸟或是对IT行业感兴趣的新人,都欢迎扫码加入我们的的圈子(技术交流、学习资源、职场吐槽、大厂内推、面试辅导),让我们一起学习成长!
g.csdnimg.cn/direct/a91b9e8100834e9291cfcf1695d8cd42.png#pic_center)
因篇幅有限,仅展示部分资料
一个人可以走的很快,但一群人才能走的更远。不论你是正从事IT行业的老鸟或是对IT行业感兴趣的新人,都欢迎扫码加入我们的的圈子(技术交流、学习资源、职场吐槽、大厂内推、面试辅导),让我们一起学习成长!
[外链图片转存中…(img-RNsUqx5w-1712649571192)]

北京人形旗下天工造物具身智能开源社区,聚焦具身天工与慧思开物两大平台
更多推荐
 11
 0
- 0


 已为社区贡献6条内容

所有评论(0)